Cookieless Attribution: How Ecommerce Brands Track Ads Without Third-Party Cookies
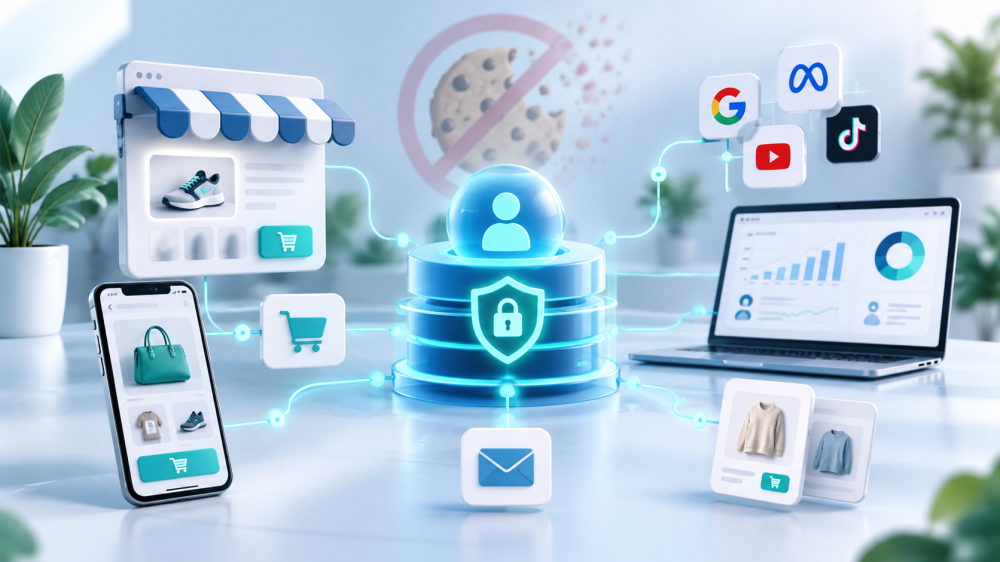
Cookieless attribution isn’t a reaction to a single deadline that already passed or is about to. It’s a rebuild of how a brand measures its ads, done because the old foundation, a browser cookie set by someone else, was never going to be reliable long term.
Brands that treat this as future-proofing tend to end up in a better position than brands waiting for one specific date to force their hand.
Where Cookie Deprecation Actually Stands in 2026
This is worth getting precisely right, because a lot of content written in 2023 and 2024 is still floating around describing a Chrome cookie apocalypse that never fully arrived.
Here’s the accurate state of things…
- Safari and Firefox have blocked third-party cookies by default for years, which on its own means roughly half the web is already effectively cookieless.
- Chrome is the outlier. Google abandoned its plan to fully deprecate third-party cookies in 2024, shifting instead to a user-choice model, and as of 2026, Chrome still has not eliminated third-party cookies by default.
- Google went even further in the other direction after that: it later scrapped the planned “choice prompt” that was supposed to let Chrome users actively opt in or out, meaning the tool most people expected to accelerate cookie loss in Chrome never shipped either.
None of that means third-party cookies are safe to build a measurement stack around.
It means the deprecation story is messier and slower than the headlines suggested, uneven across browsers, shaped as much by regulatory pressure and consent requirements as by a single hard cutoff.
The practical lesson for a brand isn’t “wait and see what Chrome does next.” It’s “don’t build anything load-bearing on a browser cookie you don’t control, regardless of which browser or which year.”
What Cookieless Tracking Methods Exist Today
Cookieless attribution isn’t one tool. It’s a stack of a few complementary pieces.
- Server-side tagging moves the actual measurement work off the browser and onto the brand’s own server, so ad blockers and browser privacy settings can’t interfere with it the way they interfere with client-side scripts.
Server-Side Google Tag Manager is the common infrastructure layer for this.
- Platform-specific server APIs send conversion data directly from the brand’s backend to each ad platform through a server-side conversions API setup: Meta’s Conversions API, Google’s Enhanced Conversions, TikTok’s Events API.
- Each works the same way in principle, sending hashed customer data like email or phone number alongside the conversion event so the platform can match it without depending on a cookie firing correctly in someone’s browser.
- First-party cookies, set on the brand’s own domain rather than a third party’s, still have a role. They’re not what’s being deprecated, and combined with server-side confirmation they remain a reasonable way to track a session.
The distinction between first-party, second-party, and third-party data is worth understanding clearly here, since the three get conflated constantly.
- Hashed identifiers and Universal IDs are the newer layer, tools like Unified ID 2.0, ID5, and LiveRamp create a standardized, privacy-compliant token from an email or phone number that participating platforms can recognize, without relying on a third-party cookie to do it.
These extend a first-party foundation. They don’t replace the need for one.

What Brands Get Wrong About “Cookieless”
A few misconceptions show up constantly, and they lead to genuinely bad decisions when left uncorrected.
“Cookieless means no cookies at all.”
Not true. Cookieless tracking mostly targets third-party cookies and the cross-site identity they enabled, not first-party cookies set on a brand’s own domain. A brand can be fully “cookieless” in the meaningful sense while still setting first-party cookies for session tracking.
“Cookieless means you can’t track anything meaningful.”
The opposite is usually true. A first-party, server-side setup built on a real customer relationship, someone who gave an email address or made a purchase, is often more accurate than a third-party cookie ever was, not less.
“Fingerprinting is a workable cookieless substitute.”
It isn’t, not anymore. Modern browsers actively randomize or suppress the device and browser signals fingerprinting depends on, and treating it as a primary attribution method carries real legal risk on top of declining accuracy.
“A Universal ID solves this by itself.”
Universal IDs are useful, but they’re an extension of a first-party foundation, not a replacement for building one. A brand that skips straight to a hashed-identifier vendor without first-party server-side infrastructure underneath it is building on a layer that has nothing solid to sit on.
Building a Tracking Stack That Doesn’t Depend on Cookies
A durable setup tends to have the same basic shape regardless of the specific tools involved.
- Start with consent management done properly, since cookieless doesn’t mean consent-free, and getting this wrong creates compliance exposure independent of anything attribution-related.
This isn’t hypothetical, regulatory changes in this space keep landing with real deadlines attached.
- Layer first-party, server-side tracking on top as the foundation, capturing events on the brand’s own domain and confirming them from the brand’s own backend rather than depending on a browser script executing successfully.
- Connect that foundation to each platform’s own server-side API, Meta CAPI, Google Enhanced Conversions, TikTok Events API, so the platforms themselves get reliable data to optimize against.
- Add Universal IDs or hashed-identifier partnerships only once that foundation exists, as an extension rather than a starting point.
Built this way, the stack doesn’t care much what Chrome decides to do next, or when. It was never depending on that decision in the first place. If you want to see what a first-party, cookieless measurement setup looks like running against your own store, book a live AdBeacon demo.
FAQ
What is cookieless attribution?
Cookieless attribution measures ad performance without relying on third-party browser cookies, typically combining server-side tracking, first-party data collection, and platform-specific server APIs like Meta’s Conversions API or Google’s Enhanced Conversions.
Are third-party cookies actually gone in 2026?
Not entirely, and not evenly. Safari and Firefox have blocked them by default for years. Chrome, the largest browser, still hasn’t eliminated them by default after abandoning its original deprecation plan in 2024 and later dropping a planned user-choice prompt as well.
Does cookieless tracking mean I can’t use any cookies?
No. Cookieless tracking specifically targets third-party cookies and the cross-site identity they enabled. First-party cookies, set on a brand’s own domain, still have a legitimate role alongside server-side tracking.
Is fingerprinting a good cookieless tracking method?
Not as a primary method. Modern browsers actively suppress the signals fingerprinting relies on, and its accuracy is probabilistic at best, with meaningful legal risk if used as anything more than a fraud-detection signal.
What should I build first for cookieless attribution?
A first-party, server-side foundation: consent management, server-side event tracking on your own domain, and platform-specific server APIs. Universal IDs and hashed-identifier partnerships are useful additions once that foundation exists, not substitutes for it.
Sources
- Consently: What Is Cookieless Tracking? Methods, Compliance, and the Post-Cookie Future
- Consentik: Google Third-Party Cookies in Chrome, Does It Still Exist?
- OneTrust: Google Drops Plans for Third-Party Cookie Choice Prompt in Chrome
- Dataslayer: Cookieless Tracking 2026, 3-Layer Setup for Marketers
- Tracklution: Cookieless Tracking Solutions, Top Methods for 2026